
SAFE Perimeter FAQs
SAFE Perimeter is a security integrator. We procure and install weapons detection screening, video, and access control — and we specialize in the layer most integrators cannot cover: continuous detection of everything transmitting in and above a site. The FAQ is grouped by the topics asked most. For specific questions for SAFE Perimeter: Airspace & Wireless Security, please contact us directly.
SAFE Perimeter — who we are and what we integrate
What does SAFE Perimeter do?
SAFE Perimeter is a security integrator. We design and install layered systems that combine walk-through weapons detection, video intelligence, and access control with the layer most integrators cannot deliver: continuous detection of everything transmitting in and above the site.
By combining device detection, movement patterns, video, and access control, we produce a complete picture of the people and devices present in an environment — not just the ones on your network.
The distinguishing idea is that cyber and physical security have stopped being separate problems. A drone over a stadium, a Flipper cloning a badge, a covert camera in an executive suite, and a rogue access point in a lobby are all one category of threat: a device operating in a space you are responsible for. Treating them with four different teams and four different tools is how the gaps appear.
SAFE Perimeter is also an authorized reseller and integration partner for LOCH Technologies, and delivers and supports the AirShield, SkyShield, SkyShield Sentry, SkyWall, NetShield AI, and LOCH Detector product lines within that framework.
Do you install cameras, access control, and weapons detection, or only wireless systems?
We do the full stack. A substantial share of our work arrives as conventional integration — walk-through weapons detection screening, video intelligence, and access control — specified, installed, and commissioned alongside everything else the site runs.
That matters for two reasons. First, most sites are buying a program rather than a product: screening at the gates, cameras through the concourse, credentials on the doors, and airspace and spectrum monitoring over all of it. Splitting that across four vendors is how the seams appear.
Second, an integrator who has already installed your screening lanes and camera network understands the site well enough to place RF sensors intelligently. Coverage design is a building problem before it is a radio problem.
Why do you focus on drone detection and wireless security?
Because it is the layer almost nobody is covering. Screening, video, and access control are mature markets with many capable providers. Airspace and RF spectrum are not — and most security integrators have no capability there at all, which leaves a gap sitting in the middle of otherwise well-defended sites.
The gap exists for a structural reason. Screening, cameras, and credentials all address people and objects crossing a physical boundary. Drones ignore that boundary entirely, and wireless devices ignore the network boundary the same way. Both categories are growing quickly, and neither is visible to a conventional physical security stack.
The result is a common and uncomfortable position: a venue with excellent screening lanes, full camera coverage, and modern access control that cannot answer a basic question about the drone that just crossed the roofline, or the transmitting device sitting in a suite. We built the practice around closing that.
Who are your clients?
Our work spans professional sports organizations and major venues, military installations and federal agencies, law enforcement and correctional facilities, critical infrastructure and utility operators, healthcare systems, data centers, gaming and hospitality properties, educational institutions, and executive protection details.
We do not publish client names. In this field the customer list is itself sensitive — knowing which venues, installations, and properties have airspace and spectrum monitoring in place is operationally useful to exactly the people those systems exist to detect. Several clients would also be prohibited by policy from appearing in a vendor's marketing regardless of their own preference.
What we can do is put you in front of a reference in your sector, with that client's consent, once a conversation is far enough along to justify the ask. That is more useful than a logo wall and considerably more honest about what it costs the reference to participate.
What does “layered security integration” mean?
It means no single tool or technique carries the program. We build multiple overlapping layers — signals intelligence, CCTV, magnetometers, access control, and physical guards — connected through a central intelligence platform, so a threat that defeats one layer is still caught by another.
The same logic operates at the sensor level within counter-UAS, where RF, acoustic, radar, and electro-optical each cover what the others miss. Layering is the answer to the same problem at both scales: any single detection method has a known blind spot, and adversaries find it.
Where is SAFE Perimeter typically deployed?
In high-value and sensitive environments where knowing who and what is present in real time carries operational weight — airports, stadiums, government and federal facilities, corporate campuses, and large-scale events.
Current deployment environments include:
- Educational institutions — schools, universities, and nonprofits
- Arenas, venues, and convention centers
- Transportation hubs — airports, seaports, rail, and bus depots
- Diplomatic premises, government, and federal facilities
- Military installations and joint interagency environments
- Retail centers, private property, and religious buildings
- Data centers, healthcare, and utility infrastructure
- Agricultural facilities and farms
- National Special Security Events (NSSEs)
Both permanent and temporary installations are supported, which is what makes the same technology work for a fixed critical-infrastructure site and a three-day event.
Have these systems been operationally tested and deployed?
Yes. SkyShield and AirShield have been deployed and evaluated at U.S. military installations, in Department of War test and evaluation activity, in joint interagency task force environments, and across critical infrastructure and large-venue sites — covering drone detection, mitigation, and wireless intrusion detection under live operational conditions rather than in a laboratory.
That operational history matters more than a specification sheet. RF environments in the field are congested, cluttered, and adversarial in ways a controlled test range is not, and detection performance that holds up on an active installation is a different claim than performance measured in isolation.
Current deployments include continuous 24-hour counter-UAS monitoring and reporting at active installations, layered fixed and mobile coverage in exercise and evaluation settings, and multi-property wireless monitoring in commercial environments.
The category — what these systems are
What is wireless airspace defense?
Wireless airspace defense is the continuous monitoring of the radio-frequency (RF) spectrum around a facility to detect, classify, and locate every emitting device in it — drones, phones, cameras, IoT sensors, rogue access points, and unauthorized cellular equipment — whether or not those devices ever touch your network.
Traditional security tools watch traffic that crosses the wire. Wireless airspace defense watches the air itself. That distinction matters because the fastest-growing categories of intrusion — covert cameras, cellular exfiltration devices, rogue base stations, and small unmanned aircraft — never authenticate to anything you control, so they generate no logs in the systems your SOC is already watching.
SAFE Perimeter covers this in two layers: AirShield for the ground-level RF and cellular attack surface, and SkyShield for the aerial layer.
What is a wireless intrusion detection system (WIDS)?
A wireless intrusion detection system (WIDS) is a sensor platform that passively monitors RF spectrum to identify unauthorized wireless devices, rogue access points, and anomalous transmission behavior inside a defined area. A WIDS detects and alerts; a wireless intrusion prevention system (WIPS) adds enforcement actions on top of that detection.
Most WIDS products on the market only listen to Wi-Fi. AirShield is built on software-defined radio (SDR) and monitors 300 MHz to 6 GHz, which brings cellular (2G through 5G, LTE, CBRS), Bluetooth and BLE, LPWAN, GPS, and drone control links into the same picture as Wi-Fi.
How is a WIDS different from the network security tools we already run?
Firewalls, NAC, EDR, and network detection and response all require a device to be on — or attempting to reach — your network. A WIDS sees devices that never connect at all. That is the entire category of threat these tools are blind to by design.
- NAC and 802.1X control what joins your network. A cellular hotspot bridging a workstation to the open internet never asks.
- EDR protects managed endpoints. A battery-powered camera behind a ceiling tile has no agent on it.
- Firewalls inspect traffic at a boundary. RF has no boundary you own.
These systems are designed to complement each other rather than compete — wireless events export to SIEM, SOAR, ITSM, CMDB, firewall, and NAC platforms so wireless events land in the same queue your analysts already work.
What is counter-UAS (C-UAS)?
Counter-unmanned aircraft systems (C-UAS) is the discipline of detecting, tracking, identifying, and — where legal authority exists — defeating unauthorized drones. The detection and tracking half is available to virtually any operator. The defeat half is tightly restricted by federal law.
Practitioners usually describe the C-UAS chain as detect → track → identify → decide → defeat. SAFE Perimeter's core offering sits in the first four steps, which is where the legal exposure is lowest and the operational value is highest: you cannot make a defensible decision about an aircraft you cannot see.
Do these systems only detect, or can they also mitigate?
Both — but the mitigation available to you depends on which layer the threat is in and what environment you operate. On the wireless layer, AirShield and NetShield AI actively respond to identified threats: isolating devices, terminating unauthorized connections, enforcing access control policy, and suppressing ports. On the aerial layer, interfering with an aircraft in flight is restricted to federal operators holding statutory authority.
That split is the single most consequential thing to understand before scoping a program, because the two layers sit under entirely different bodies of law:
- Wireless mitigation is a network security action against devices and connections in your own environment. It is available to commercial, critical infrastructure, law enforcement, and military operators alike, within the limits described in the wireless panel.
- Aerial mitigation — jamming, spoofing, or kinetic defeat of an unmanned aircraft — requires federal authority under statute. Private operators do not hold it.
SAFE Perimeter fields both. What we scope for a given customer is driven by what that customer can lawfully operate.
Do these systems emit or interfere with our Wi-Fi, cellular, or medical equipment?
The detection platforms are passive. AirShield and SkyShield receive RF; they do not emit signals that would interfere with Wi-Fi, cellular service, aviation systems, or medical equipment. SkyShield Sentry is likewise non-RF-emitting, using acoustic sensing instead.
This matters in three environments in particular: hospitals with sensitive biomedical equipment, airports and seaports operating under aviation spectrum rules, and SCIFs and other no-wireless zones where an emitting sensor would be self-defeating.
Drones over your property — what is and isn’t legal
How do I know if a drone is watching my property?
A drone conducting surveillance is usually detectable well before it is visible. RF detection identifies the control link, classifies the airframe model, tracks the flight path, and geolocates the operator — producing a record of what was overhead, when, for how long, and who was flying it.
Visual and audible cues are unreliable on their own. Modern aircraft operate at altitudes where they are hard to see and increasingly hard to hear, and repeated overflights are difficult to distinguish from transient traffic without a log.
The distinction that matters is between a single pass and a pattern. One overflight is usually nothing. The same airframe, at the same hour, over the same building, across multiple days is surveillance — and it is only visible to someone keeping a record.
Can I shoot down a drone over my property?
No. Federal law classifies drones as aircraft, and shooting at one violates 18 U.S.C. § 32 — a felony carrying up to 20 years in prison, alongside FAA civil penalties. The same rule covers pointing a laser at a drone. The airspace above your property is regulated by the FAA, not owned by you.
The exposure compounds beyond the federal charge. A downed aircraft can injure someone or damage property, opening state and local charges, and the operator can sue you for destroying theirs.
What you can lawfully do is detect, identify, document, and report:
- Detect and classify the aircraft — model, flight path, time on station
- Geolocate the operator, who is frequently the actionable element, not the drone
- Document with time-stamped records that support a police report, a restraining order, or a prosecution
- Report to local law enforcement or the FAA, who hold the authority to act
This is precisely why detection systems exist. An aircraft you cannot see, identify, or attribute leaves you with no lawful options at all. One you have tracked and attributed gives law enforcement something to work with.
Is it legal to detect drones and unauthorized wireless devices on our property?
Passive RF detection — listening to the spectrum without transmitting or interfering — is generally lawful for private and commercial operators in the United States. Active measures are not. Because detection systems can capture information about communications, most organizations still need to align deployment with wiretap, privacy, and employment law before turning a system on.
Two rules of thumb that hold up across most jurisdictions:
- Listening is different from interfering. Non-emitting sensors that classify signals do not implicate the statutes that govern jamming.
- Metadata is different from content. Detecting that a device is transmitting is a different legal question than capturing what it transmitted.
SAFE Perimeter is not a law firm and this is not legal advice. We recommend every deployment be reviewed by your own counsel, and we will support that review with technical documentation of exactly what a system does and does not collect.
How does SAFE Perimeter protect privacy?
Security and privacy have to coexist, and the system is built on that premise. It operates within legal authority and regulatory compliance, collects anonymized data from Wi-Fi, Bluetooth, and RFID emissions in the same manner as standard network operations, and never shares personal data without authorization.
The technical point that resolves most concern: these are RF sensors, not content interception. They observe that a device is transmitting, what type it is, and where it sits. They are not reading messages, listening to calls, or identifying individuals by name.
- Anonymized collection from Wi-Fi, Bluetooth, and RFID emissions
- Computer-vision integrations follow current industry privacy compliance practice
- Threat detection lists built on lawful and ethical criteria, focused on risk rather than individuals
- Deployment scoped and documented so your counsel can review exactly what is and is not collected
SAFE Perimeter is not a law firm and this is not legal advice. We recommend every deployment be reviewed by your own counsel, and we support that review with technical documentation of the actual data footprint.
Scoping, cost, and support
Can the system be customized and scaled to our site?
Yes. Perimeter size and coverage, detection sensitivity by zone, integration with equipment you already run, and alert and notification rules are all configurable to the environment. Sensitivity is commonly tuned differently for a high-traffic public concourse than for a restricted zone in the same building.
Scaling is additive: permanent systems expand by adding sensors as coverage requirements grow, and temporary installations can extend a permanent footprint for events, rooftop monitoring, or high-profile gatherings without re-architecting anything.
Do you offer managed services, or do we operate the system ourselves?
Both. Organizations with a staffed SOC typically operate the platform directly with our training and support. Those without one use SAFE Perimeter's managed offerings — risk assessments, 24/7 NOC and managed services, operational support, and Drone Detection as a Service (DDaaS).
DDaaS is often the right entry point for organizations that need airspace awareness but cannot justify standing up an internal counter-UAS function: the capability is delivered as a service, with monitoring and reporting handled for you.
Comprehensive operator training is provided in every configuration, scoped to the systems fielded and the roles that will use them.
How much does a drone detection system cost?
Published market ranges run from roughly $10,000 for a basic single-sensor setup to $500,000 and beyond for fixed multi-sensor sites, with full detect-track-identify-mitigate programs climbing higher. Coverage area and required reliability drive price far more than any single specification on a datasheet.
The variables that actually move a quote:
- Coverage geometry — sensor count follows terrain, building materials, and where the protected space sits, not square footage
- Layers — RF alone costs less than RF plus acoustic plus radar, and covers less
- Mitigation — adds hardware cost and a regulatory approval path
- Integration — feeding an existing C2 or SOC costs less than standing up a new console
- Sustainment — annual maintenance commonly runs 10–15% of hardware cost, and belongs in a five-year total-cost view rather than the purchase price
SkyShield and AirShield pricing is scoped after a site assessment, because quoting a counter-UAS system off a floor plan produces a number that changes once someone measures the actual RF environment.
How do organizations purchase SAFE Perimeter systems?
Federal, state, and local buyers can acquire product lines through GSA Schedule via our distribution partners. Commercial and critical-infrastructure buyers contract directly with SAFE Perimeter or through an authorized channel partner.
Most engagements start the same way regardless of path: a scoped site assessment that establishes what is actually emitting in your environment today. That assessment usually determines sensor count and placement more reliably than square footage alone.
Every environment has a different RF baseline. The fastest way to know what you are dealing with is a scoped site assessment.
Request a site assessmentFor enterprise security, corporate security, gaming and hospitality, healthcare, data centers, retail, and critical infrastructure operators. Focus: weapons detection screening, video and access control, wireless intrusion detection, covert device discovery, and the vertical questions we hear most — schools, venues, executive protection and critical infrastructure.
Screening, video, and access control
What weapons detection screening do you install?
We specify, install, and commission walk-through weapons detection screening for venues, schools, corporate campuses, healthcare, and government facilities — including lane design, throughput planning, staffing model, and secondary screening procedure.
The decision that governs everything else is throughput against sensitivity. Screening tuned to catch everything stops everyone, and a queue outside the doors is its own security problem. Screening tuned for speed misses things. Getting that balance right depends on your actual entry volume, peak arrival pattern, and what you are genuinely trying to intercept.
Lane count, placement, and the secondary screening path usually matter more to real-world performance than the specification of the units themselves.
Do you integrate with cameras and access control we already own?
Yes, and that is usually the better outcome. Most sites already have a video management system and an access control platform with years of configuration behind them. Replacing working infrastructure is expensive and rarely necessary; connecting it is what produces the picture nobody currently has.
Integration work typically covers video management systems, access control and credentialing platforms, intrusion and alarm panels, mass notification, and the security operations centre workflow that ties them together.
The value is in the correlation. A badge read, a camera view, and a wireless device appearing in a restricted area are three separate records in three separate systems. Together they are an incident — and no one system can see it alone.
Why does a security integrator need wireless and airspace detection?
Because screening, video, and access control all address people and objects crossing a physical boundary, and the fastest-growing threat categories do not cross one. A drone flies over it. A transmitting device is carried through in a pocket that no magnetometer will alarm on.
This produces a familiar gap: a site with excellent screening lanes, full camera coverage, and modern credentialing that cannot answer a basic question about the aircraft that just crossed the roofline, or the device transmitting from a suite it should not be in.
Most integrators have no capability in that layer at all. Adding it is what turns a well-built physical program into a complete one — which is why we lead with it, and why we also install the rest.
Wireless intrusion detection — how it works
What is AirShield?
AirShield is a broad-spectrum wireless intrusion detection sensor built on software-defined radio. It continuously monitors 300 MHz to 6 GHz to discover, classify, and locate every emitting device in a facility — across Wi-Fi, cellular, Bluetooth and BLE, LPWAN, GPS, and drone control links — without requiring any of those devices to be on your network.
A single AirShield sensor covers roughly 25,000 square feet. Sensors are PoE-powered, mount permanently, and connect to a cloud portal with no on-premise server required. LTE backhaul is available where running the sensor through your production network is undesirable.
The output is a live inventory of your wireless environment: what is transmitting, what protocol it speaks, what vendor made it, where it sits, and whether its behavior has changed.
What is a software-defined radio, and why does it matter?
A software-defined radio is a receiver whose tuning is handled in software rather than fixed in hardware. One physical sensor can therefore listen across many different kinds of signal — Wi-Fi, Bluetooth, cellular, GPS, drone control links — instead of needing a separate purpose-built box for each.
The everyday comparison is a car radio that only receives FM versus a device that can be told, in software, to receive anything. The first is finished the day it ships. The second is defined by its instructions.
Two practical consequences for a buyer:
- Coverage. One AirShield sensor covers 300 MHz to 6 GHz — essentially the whole commercial spectrum — instead of covering Wi-Fi and calling that wireless security.
- Longevity. When a new protocol or a new threat device appears, support usually arrives as a software update rather than a hardware replacement. A fixed-function radio would need to be ripped out and re-bought.
That second point is what makes the difference over a five-year horizon. The wireless threat landscape moves faster than procurement cycles, and equipment that can only be updated by replacement falls behind.
What wireless threats do firewalls and network monitoring miss?
Anything that transmits but never connects. In practice that means covert cameras and audio devices, cellular hotspots bridging around network controls, rogue and evil-twin access points, unauthorized cellular base stations, embedded radios inside newly delivered equipment, drone control links, and GPS interference.
The unifying property is that none of these produce a log entry in a system you already own. They are invisible to network-layer tooling not because the tooling is weak, but because there is nothing on the network to see.
With the large majority of IoT devices now connecting wirelessly, the gap between "devices on our network" and "devices in our building" keeps widening — and only one of those two is instrumented at most organizations.
What we find — covert devices and rogue infrastructure
How do you find a hidden camera or listening device?
Covert cameras and audio devices are found by their transmissions, not by looking for them. Any device that streams or uploads must emit — over Wi-Fi, Bluetooth, or cellular — and the sensor classifies that emission by protocol, vendor, and behavioral pattern, then localizes it so a security team can physically recover the device.
This is materially more reliable than the two conventional approaches. Physical searches miss devices concealed in fixtures, vents, and furniture. Handheld RF detectors give a proximity reading with no classification, no history, and no way to distinguish a covert camera from a guest's phone.
Continuous monitoring also catches the case a periodic sweep cannot: a device installed the day after your last sweep, or one that only transmits during a specific meeting.
Can you detect a Flipper Zero, a Bluetooth skimmer, or smart glasses?
Yes. Multi-tool devices like the Flipper Zero, Bluetooth-based card skimmers, and camera-equipped smart glasses all emit, and emission is what AirShield classifies. Each is identified by protocol behavior and device signature rather than by appearance, which matters because none of them look like an attack tool.
These have become the practical threat set in public-facing environments:
- Multi-tool RF devices — used against access control, RFID badging, and sub-GHz building systems
- Bluetooth skimmers — placed on payment terminals and fuel pumps, transmitting captured card data
- Smart glasses and wearable cameras — recording in areas where phones would be challenged but eyewear is not
- Spoofed captive portals — harvesting credentials from patrons who believe they are on venue Wi-Fi
The common thread is that traditional security controls have no way to see any of them. A guard cannot spot a skimmer, a camera cannot see a Bluetooth transmission, and a firewall never sees traffic that does not touch the network.
What is a rogue access point or evil twin, and how is it detected?
A rogue access point is an unauthorized wireless access point operating inside your environment. An evil twin is a rogue AP deliberately impersonating your legitimate network so that people and devices connect to it and route their traffic through an attacker. Both are identified by comparing observed RF characteristics against your authorized device inventory.
Impersonation is the harder problem: the SSID matches, so the endpoint sees nothing wrong. Detection has to happen at the radio layer — comparing signal characteristics, physical location, and behavior against the known-good baseline for your own infrastructure.
This is a recurring finding in high-traffic venues where third-party wireless installations, vendor kiosks, and tenant equipment create a large and poorly-inventoried footprint.
How do you detect a stingray, IMSI catcher, or fake cell tower?
Yes. The sensors monitor cellular and CBRS spectrum and identify unclassified or unexpected cell towers operating in your environment — the signature of a rogue base station used to intercept mobile traffic through a man-in-the-middle attack.
Cellular is the blind spot most enterprises have never instrumented. Every employee, contractor, and visitor carries a device that can be induced onto a hostile base station, and none of that traffic touches your network or your controls.
Spectrum graphs show band occupancy and density, which lets teams identify unexpected cellular devices and enforce no-wireless policy in restricted areas.
What is shadow IoT, and why is it a security risk?
Shadow IoT is the population of connected devices operating inside an organization without IT's knowledge or approval — smart TVs, building sensors, wireless printers, cameras, environmental controls, and vendor-installed equipment. These devices introduce operating systems, protocols, and frequencies the security team has never inventoried.
Two things make it dangerous. First, these devices are rarely patched and often ship with default credentials. Second, and less obviously, embedded radios arrive inside equipment nobody thought of as a network device — LOCH has found Wi-Fi, cellular, and Bluetooth modules inside newly delivered equipment during deployment, and a transmitting camera operating inside a customer clean room.
What is the difference between AirShield and AirShield-Mini?
AirShield is the full-spectrum sensor: cellular, Wi-Fi, and Bluetooth across roughly 25,000 square feet, with broad SDR coverage and a rugged permanent-mount enclosure. AirShield-Mini is a compact plug-in unit covering Wi-Fi and Bluetooth only across roughly 1,500 square feet, with no cellular or SDR coverage.
The selection rule is straightforward: if the threat model includes cellular exfiltration, rogue base stations, or drone control links, you need full AirShield. Mini is for extending Wi-Fi and Bluetooth visibility into microzones — tenant retail units, kiosks, individual suites — where full-spectrum coverage is already established nearby.
Can AirShield detect GPS jamming or spoofing?
Yes. The sensors monitor GPS signal integrity and flag interference and anomalous behavior in the GNSS bands, which is how both jamming and spoofing present in the RF environment.
This matters wherever timing or position feeds an operational system: logistics and yard operations, financial and telecom infrastructure that depends on GPS for time synchronization, port and terminal operations, and any facility where autonomous or semi-autonomous vehicles navigate.
Autonomous monitoring and automated response
Can AirShield actively stop a wireless threat, or does it only alert?
It does both. Beyond detection, the platform enforces policy against identified threats — terminating unauthorized wireless connections, isolating devices to prevent lateral movement, validating that access control lists are blocking on network switches, and testing port suppression to disable devices on the Ethernet network. Enforcement can be triggered manually or automatically on a policy violation.
This is the difference between a wireless intrusion detection system (WIDS) and a wireless intrusion prevention system (WIPS). Our deployments operate as both, which is why they belong in a response workflow rather than only in a monitoring dashboard.
The important scoping question is what you enforce against. Action taken against an identified threat to your own environment, as part of reasonable network management, sits on very different footing than blanket interference with communications you do not control. The FCC has enforced against the latter under Section 333 of the Communications Act, and in those matters the Commission specifically noted the absence of any identified security threat that would have justified the action. Threat-triggered enforcement as part of reasonable network management is a different posture than blanket blocking. Policy configuration is therefore part of deployment, not an afterthought.
Can you detect a threat before it happens?
Often, yes — because preparation emits. Analyzing the flow of devices and people surfaces unusual behavior before it escalates: an unauthorized device appearing repeatedly at the same hour, a drone controller powering up miles outside the perimeter, a device probing wireless infrastructure, or an abnormal movement pattern in a restricted zone.
Counter-UAS is the clearest illustration. Detection triggers on the control link during power-up and pre-flight, so an aircraft is frequently visible before it leaves the ground. That is a window for intervention rather than a record of an incident.
The same holds on the wireless side. Reconnaissance precedes exploitation, and reconnaissance is visible in the RF environment to anyone instrumented to see it.
What does “autonomous monitoring” actually mean?
It means nobody has to be watching a screen for the system to do its job. The sensors listen continuously, NetShield AI decides what matters, and a person is contacted only when something needs a person. On a quiet night, no one is bothered.
The plain version of the problem: a site covering a few hundred thousand square feet produces tens of thousands of wireless events a day. Nearly all of it is staff phones, guest devices, printers, and building sensors doing exactly what they should. A human being cannot read that, and a system that alerts on all of it gets muted within a week.
So the software learns what normal looks like at your site — which devices belong, where they usually are, what hours they keep — and raises only the departures from it. A device that has never been here before, sitting outside the executive floor at 2 a.m. A drone controller powering up across the road. A camera transmitting from a room that should have no camera in it.
What your team gets is a phone alert with the specific thing, the specific place, and the recommended action — not a dashboard to interpret.
What is NetShield AI?
NetShield AI is the agentic analytics layer that sits on top of the sensor network. It ingests data from AirShield, SkyShield, and connected security tooling, correlates events across the RF and aerial layers, and drives automated response rather than leaving correlation to an analyst.
The problem it solves is volume. A broad-spectrum sensor covering 300 MHz to 6 GHz across a large site produces far more events than a security team can triage manually, and the meaningful signal is usually a pattern across events rather than any single one — a device that appears at the same hour each week, a drone control link that precedes a wireless probe, a cellular anomaly correlated with a physical access event.
NetShield AI raises what matters, suppresses what does not, and executes the response policy your team has defined.
Schools and universities
What does school security cost, and where should a district start?
Start with whichever layer you can fund without a capital project, because a plan nobody can pay for protects nobody. Software running on cameras a district already owns is usually the cheapest entry point; wireless monitoring in one high-value area is next; walk-through screening is the largest commitment because of hardware, lanes and daily staffing.
Staffing is the part districts consistently underestimate. We size it before you commit rather than after. Full detail on the schools page.
Will weapons detection screening slow down arrival at a school?
That depends on lane count and placement, not on the equipment. We plan against your real arrival volume and peak pattern before anything is ordered.
Under-lane a building and the queue outside becomes its own safety problem, which is why throughput is part of the design rather than something discovered in week one.
Does wireless monitoring in a school mean monitoring students?
No. The sensors observe that a device is transmitting, what type it is and roughly where it sits. There are no messages, no browsing history, no names, and no software installed on any student device.
Collection is anonymized. We recommend districts adopt a written board policy covering collection, access and retention before the first sensor is installed.
Can a school district stop a drone flying over campus?
No, and neither can anyone else selling to a school district. Interfering with an aircraft in flight is restricted to a limited set of federal agencies, and jamming or shooting at a drone is a federal offense.
What a district can lawfully do is detect the aircraft, identify the model, track its path and locate the operator so a school resource officer or law enforcement has something to act on.
Do schools have to replace existing cameras and door hardware?
No. Detection software runs on cameras a district already owns, provided image quality holds at the distances involved, and existing access control is integrated rather than swapped out.
Where equipment genuinely cannot carry the load, we say so early rather than after a purchase order.
Executive protection and VIP
What does wireless counter-surveillance actually find around a principal?
Hidden cameras concealed in rooms, fixtures, vehicles and gifts. Listening devices on or off the network. Cell interceptors positioned to capture calls and device identity. GPS trackers on vehicles, luggage and personal effects. Rogue and evil-twin networks. Camera-equipped wearables. And drones over property lines, helipads and arrivals.
The common thread is that all of it emits, and none of it is visible to a detail controlling doors, routes and rooms. More on the executive protection page.
How is this different from a traditional TSCM sweep?
A sweep is a moment in time. It is scheduled, expensive, dependent on the specialist in the room, often limited to Wi-Fi and Bluetooth, and it leaves little forensic record. The room is clean when they leave and can be re-compromised minutes later.
Continuous monitoring is a posture rather than a visit: passive across 300 MHz to 6 GHz, surfacing threats in minutes with the device located for retrieval, and producing a time-stamped log that can be replayed after the fact.
Does the system travel with the principal?
Yes. A discreet enclosure covers a residence, office, aircraft or vessel, and an executive backpack carries the same capability through hotels, airports and unfamiliar rooms.
Nothing is on show and nothing needs explaining to a host or a guest. Because the sensors are entirely passive, they give away no signature of their own.
Can smart glasses and wearable cameras be detected?
Yes. Camera-equipped eyewear and body-worn recorders emit like any other device and are identified by protocol behavior and device signature rather than by appearance.
That matters because appearance is exactly what they are designed to defeat. In a boardroom or a private dinner, nobody asks a guest to remove their glasses.
Stadiums, venues and events
What are the main wireless and airspace threats at a stadium?
Drones over fans, players and press areas for observation or livestream piracy. Rogue access points and spoofed captive portals harvesting credentials. Bluetooth skimmers at points of sale. Covert cameras in locker rooms and executive suites. And illegal jammers deployed against alarms, radios or wireless payment during an incident.
None of it produces a log entry in a system a venue already owns. Detail on the stadiums and events page.
Can a venue cover an event without buying permanent hardware?
Yes. Mobile kits deploy from a vehicle or hardcase with no installation, which suits event-day surge, temporary venues and training camps.
For fixed venues hosting periodic events, a hybrid is usually better economics: permanent sensors over the core footprint, with mobile kits extending coverage to parking, overflow and perimeter approaches on event days. Managed coverage is also available through Drone Detection as a Service.
Who operates the system on game day?
Either your team or ours. Where a venue wants trained personnel on post, we place licensed officers through our guard services partnership who are briefed on the detection stack they are working alongside.
An officer who understands what an RF or airspace alert represents responds correctly the first time, rather than escalating everything or ignoring what looks unfamiliar.
Critical infrastructure and utilities
What is the wireless blind spot at a critical infrastructure site?
A refinery, hospital, data center or treatment plant is fenced, badged and patrolled. Its wireless perimeter and its control network usually are not. Contractor hotspots, wireless field instruments, legacy connected devices and internet-facing controllers are all entry points, and most operators have no continuous way to see them.
Coverage across sectors is set out on the critical infrastructure page.
Is passive monitoring safe for control systems and medical devices?
Yes, and it is the reason discovery here has to be listen-only. Active scanning is unsafe for fragile control systems and clinical equipment that cannot tolerate being probed.
Our sensors receive only. They transmit nothing, so they cannot interfere with SCADA timing, medical telemetry, production systems or spectrum authorizations.
Does continuous monitoring help with compliance?
It produces the two things auditors and regulators increasingly ask for and most operators cannot supply: an asset inventory that includes unmanaged devices, and a time-stamped record of the wireless environment.
Several frameworks already require rogue-wireless scanning that is performed manually and periodically today. Continuous monitoring replaces that exercise with exportable, audit-ready evidence.
Integration, deployment, and compliance
Does AirShield integrate with our SIEM and SOC workflow?
Yes. The platform integrates with SIEM, SOAR, ITSM and ITSL, CMDB, firewall, and NAC platforms through API-based connectors, so wireless events flow into the same ticketing and response workflow your analysts already use.
It also maintains historical RF event logs for forensic review — time-synced records that support incident investigation, compliance reporting, insurance claims, and litigation. In practice the forensic record is often what justifies the program internally, because it converts "we think something happened" into a defensible timeline.
Do we need to install agents or tap our network?
No. The sensors require no software on endpoints, no network tap, and no on-premise server. Sensors observe the RF environment directly and report to a cloud portal. Where connecting sensors to the production network is undesirable, they can backhaul over LTE instead.
This is why deployments move quickly — there is no agent rollout, no change window on production infrastructure, and no dependency on the network you are trying to assess.
How does this apply to gaming, hospitality, and large venues?
Gaming and hospitality properties combine the hardest conditions in wireless security: enormous floor area across dozens of zones, extremely high device turnover from transient guests, third-party wireless installations outside direct IT control, and guest-privacy exposure in rooms, restrooms, and convention space.
In deployed gaming and hospitality environments, LOCH sensors have identified fake access points and rogue cell towers impersonating authorized networks, weak third-party wireless installations that were trivially attackable, and a connected camera transmitting from a restroom. Sensors have been deployed across multiple properties with data feeding into network detection and response tooling, and have defended a property hosting one of the largest hacker conventions in the world.
The operational value is continuity: monitoring for policy violations, long-running new devices and networks, and changes in DAS and tower deployments, rather than a point-in-time sweep that is stale the day after it finishes.
How does wireless monitoring support compliance and cyber insurance?
Continuous wireless monitoring produces the two things auditors and underwriters increasingly ask for and most organizations cannot supply: a complete asset inventory that includes unmanaged devices, and a time-stamped forensic record of the wireless environment.
Asset inventory is a control requirement in essentially every major framework, and an inventory that excludes everything not on the network is an incomplete one. On the insurance side, carriers are tightening requirements around demonstrated visibility, and RF event logs give you evidence rather than assertion when a claim is reviewed.
What does a deployment actually look like?
Most commercial engagements run in three stages: a scoped site assessment that baselines what is emitting today, a sensor design that sets count and placement against that baseline, and installation with SIEM integration and analyst handover.
Sensor count is driven by coverage geometry, not just square footage — building materials, floor separation, and where the sensitive space actually sits all move the number. This is why we assess before quoting rather than pricing off a floor plan.
If you have never baselined your RF environment, the first assessment is usually the most informative security exercise your team runs that year.
Talk to SAFE PerimeterFor the Department of War (DoW), installation defense, National Guard, federal agencies, and critical infrastructure with a federal nexus. Focus: layered counter-UAS detection, sensor fusion, and integration with the common operating picture.
Layered counter-UAS — the architecture
What is layered drone detection, and why isn't one sensor enough?
Layered detection means running complementary sensing modalities — RF, acoustic, radar, and electro-optical — so that a threat defeating one modality is still caught by another. No single modality covers the full threat set, because each one is blind to a specific and well-understood class of aircraft.
- RF detects the control link and often geolocates the operator, but not an aircraft flying a pre-loaded waypoint mission with its radio off.
- Radar sees physical returns, but small drones flying low against clutter sit at the edge of its performance envelope.
- Acoustic detects the one signature a flying object cannot suppress, but at shorter range.
- EO/IR confirms and identifies visually, but needs a cue and clear line of sight.
Adversaries adapt to whatever you field. Layering is what keeps a single countermeasure from collapsing your entire detection picture.
What is Remote ID, and what does it broadcast?
Remote ID is the FAA rule, codified at 14 CFR Part 89, requiring most drones to broadcast identification and location while operating outdoors. It is often described as a digital license plate: any compatible receiver nearby can read the drone's serial number, its position and altitude, and the position of its control station.
Enforcement has been in effect since March 16, 2024, with no grace period, and civil penalties reach $27,500 per violation. Compliance comes either built into the aircraft — most DJI models released since 2022 — or through an add-on broadcast module.
One detail that matters operationally: the broadcast itself does not identify the owner. Only authorized agencies can connect a broadcast serial number to the registration record behind it.
Is Remote ID enough for drone detection?
For airspace awareness, it is often sufficient. For security, it is not. Remote ID is a cooperative system — it reports drones whose operators chose to comply. Nearly every category of aircraft a security program exists to catch is either exempt from the rule or non-compliant by design.
The closest analogy is ADS-B in manned aviation. ADS-B gives controllers an excellent picture of cooperative traffic, and no serious airspace security program treats it as a substitute for primary radar. Remote ID occupies the same position for drones.
What Remote ID does not show you:
- Drones with Remote ID disabled, spoofed, or never installed. An operator smuggling contraband into a correctional facility has strong incentive to be invisible and no incentive to broadcast.
- Aircraft under 250g flown recreationally — the DJI Mini class — which are unregistered and exempt.
- Operations at FAA-Recognized Identification Areas (FRIAs), which are exempt by design.
- DIY, home-built, and modified airframes, which carry no compliant module.
- Anything indoors, since the rule covers outdoor operation only.
- Foreign and adversary systems, which are not subject to FAA rulemaking at all.
Receiver range is also environment-dependent in a way spec sheets rarely convey. Broadcast Remote ID is a short-range signal, and a handheld receiver in dense urban terrain covers a fraction of what a mast-mounted sensor covers in open ground. SkyShield LR detects control links out to 14 km, frequently before an aircraft leaves the ground.
The right answer is to use both. Remote ID is a genuinely valuable layer, and the strongest architecture ingests it: compliant traffic gets whitelisted and stops generating alerts, so operators spend their attention on the non-cooperative contacts that RF, acoustic, and radar sensing surface. Remote ID tells you about the drones following the rules. SkyShield tells you about the ones that aren't.
What are Group 1 and Group 2 UAS?
The DoD classifies unmanned aircraft into five groups by weight, operating altitude, and speed. Group 1 covers aircraft under 20 lbs operating below 1,200 feet AGL at under roughly 100 knots. Group 2 covers 21 to 55 lbs, below 3,500 feet AGL, at up to roughly 250 knots.
Detection approach differs between them. Group 1 detection typically relies on RF spectrum monitoring, acoustic sensing, electro-optical, or Wi-Fi and cellular signature identification. Group 2 generally requires RF direction finding, multi-sensor fusion combining RF with radar and EO/IR, and data-link fingerprinting.
Group 1 is where the majority of the installation-defense and critical-infrastructure problem sits today — commercial quadcopters used for surveillance, payload delivery, and perimeter probing.
RF drone detection
What is SkyShield?
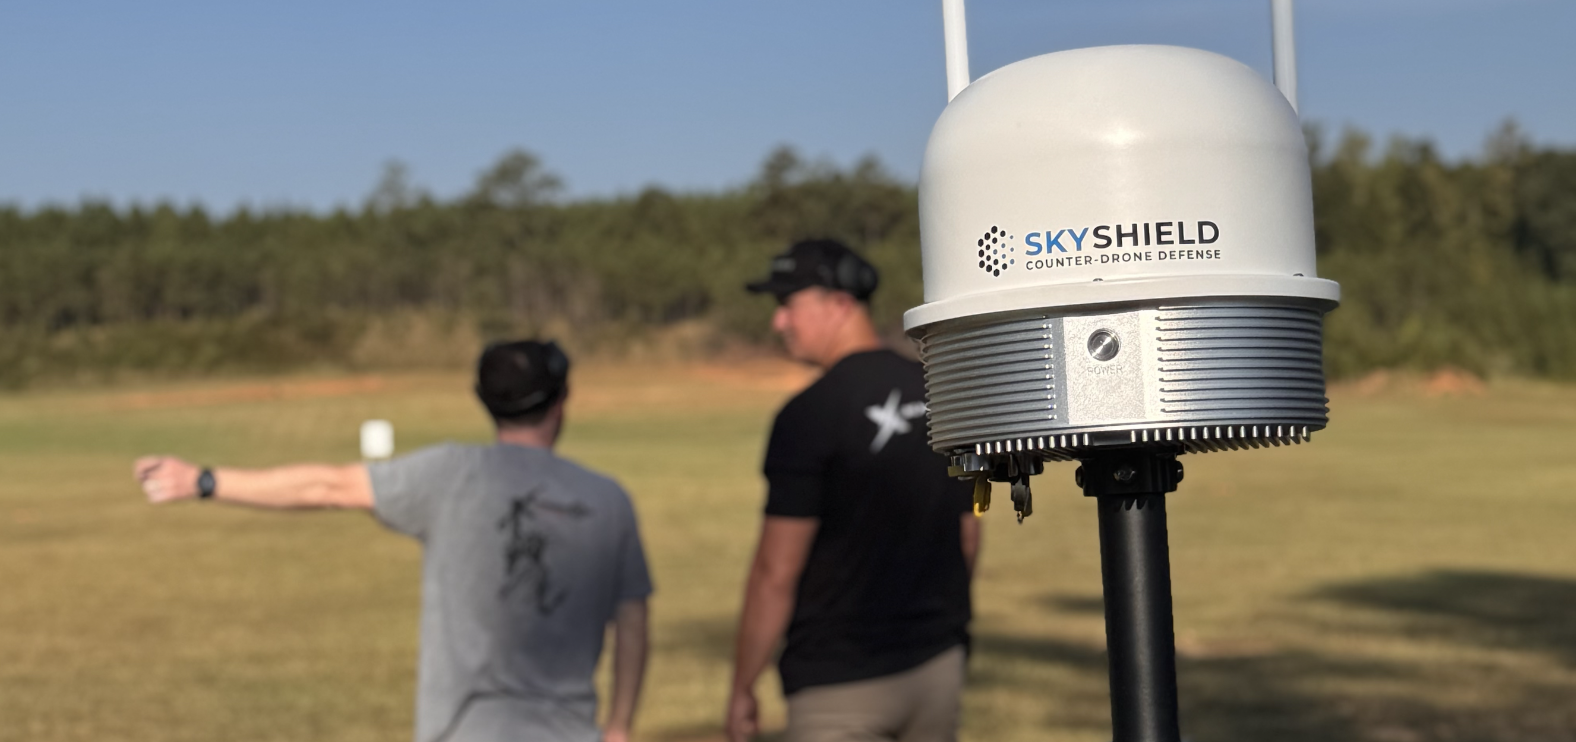
SkyShield is an RF-based counter-UAS detection system that detects, tracks, classifies, and geolocates unauthorized drones and their operators. It uses AI-enabled signal classification against a library of more than 500 known threat models, covering commercial, hobbyist, and DIY-built aircraft.
The fixed and mountable SkyShield LR configuration supports detection from 7 to 14 km depending on configuration and environment, across 2.4 GHz, 5.2 GHz, 5.8 GHz, 915 MHz, 868 MHz, and 433 MHz, with RF direction finding, 360-degree airspace coverage, and near-zero false alarms. It emits nothing. Situational awareness is delivered to both desktop and mobile applications.
It can be permanently mounted to infrastructure, vehicles, or aircraft, or deployed rapidly from a transport case.
How far away can a drone be detected?
SkyShield LR detects RF control links from 7 to 14 km — roughly 4.5 to 8.7 miles — depending on configuration and environment. SkyShield Mobile reaches 3 to 7 km. SkyShield Sentry detects acoustically to 2,000 m. In practice, detection frequently happens before takeoff, because the control link is active during power-up and pre-flight while the aircraft is still on the ground.
Treat any published range as a ceiling rather than a guarantee. Real sites add clutter, RF congestion, terrain, and obstructions that spec-sheet figures measured in open ground do not account for. Low-flying aircraft are harder to detect at distance than high ones, and hills, tree lines, and buildings create genuine blind spots.
Which is the argument for layering. Range is one modality's strength; another modality's strength is seeing what the first one structurally cannot.
What is the difference between SkyShield LR, SkyShield Mobile, and SkyShield Sentry?
They solve three different problems. LR is the fixed long-range dome for persistent site coverage. Mobile is a ruggedized handheld and backpack-portable kit for tactical and expeditionary use, covering 3 to 7 km. Sentry is the acoustic system that detects aircraft RF cannot see.
- SkyShield LR — 7 to 14 km, fixed or vehicle-mounted, MIL-STD RF hardware, 360-degree coverage, roughly 25 lbs with case.
- SkyShield Mobile — 3 to 7 km, handheld with direction-finding antennas, MOLLE-compatible, roughly 4.5 hours of battery on DF antennas or up to 6 on omnidirectional, ATAK-compatible.
- SkyShield Sentry — acoustic detection to 2,000 m, non-RF-emitting, with AI-enabled targeting and autonomous interceptor management through a centralized C2 console.
Most installation-defense architectures use LR for the persistent picture and Mobile for patrol, response, and forward elements, with Sentry added where the threat set includes non-emitting aircraft.
Can SkyShield locate the operator, not just the aircraft?
Yes. RF direction finding on the control link lets SkyShield geolocate the remote controller as well as the aircraft, and identify aircraft by unique device ID.
Operationally this is often the more valuable output. An aircraft overhead is a symptom; the operator is the actionable target — the person a response team can lawfully contact, and the element that turns a detection into an investigation rather than an observation.
Because detection triggers on the control link rather than the airframe, the system frequently sees aircraft during power-up and pre-flight — before takeoff, and at standoff distances well outside a perimeter.
Does SkyShield integrate with ATAK and existing C2 systems?
Yes. SkyShield Mobile pushes live contacts into ATAK, and the platform exposes simple APIs for integration with digital battle management systems. It is compatible with tactical MANET radios. SkyShield Sentry is network-ready for integration with external C2 systems.
Integration is usually the deciding factor in operational adoption. A sensor that requires an operator to watch a dedicated screen adds a task; a sensor that pushes contacts into the common operating picture the unit is already running adds capability without adding manning.
Acoustic detection of non-emitting drones
Can you detect drones that don't emit RF?
Yes — that is what SkyShield Sentry exists for. Fiber-optic tethered drones and pre-programmed autonomous aircraft are specifically designed to defeat RF and GPS-based counter-UAS: no control link to intercept, no GPS dependency, low-altitude flight below radar coverage, and minimal electronic signature.
Sentry detects them acoustically. Any aircraft that flies must move air, and moving air makes sound. Sentry uses acoustic sensing with AI classification, optimized for the low-RPM, low-signature flight profiles tethered platforms produce, with sensor fusion across modalities, direction finding and range estimation, high clutter rejection, and full operation in GPS-denied and RF-congested environments.
The design premise is simple: tethered drones defeat electronic detection, but they cannot defeat physics.
Mitigation, authority, and terminology
Is this electronic warfare?
Parts of the portfolio are, and parts are not — and the distinction is doctrinal rather than promotional. In electromagnetic spectrum operations, electronic warfare divides into electronic support, electronic protection, and electronic attack. SkyShield and AirShield perform electronic support and contribute directly to electronic protection. SkyWall is an electronic attack capability, and is fielded only to operators with the authority to employ one.
AirShield and NetShield AI additionally provide active mitigation at the network layer — terminating unauthorized connections and enforcing policy against identified threats — which is a security enforcement action rather than an electronic attack.
We are precise about this for an operational reason. A requirements owner who hears "electronic warfare" applied to a receive-only sensor will discount the claim, and one who hears it applied to a network enforcement action will assume a spectrum-interference problem that does not exist. Describing each capability by what it actually does — support, protection, network enforcement, or attack — is what keeps a program moving through the right approval chain.
What about drone mitigation and defeat?
SAFE Perimeter fields aerial mitigation capability for customers with the legal authority to operate it. (Wireless-layer mitigation is a separate matter and is available far more broadly — see the commercial panel.) SkyWall is an RF counter-UAS mitigation system providing 360-degree protection to a radius of 2 to 3 km, with automated, manual wideband, and smart selective modes when integrated with SkyShield detection and direction finding. SkyShield Sentry provides non-RF kinetic interception.
These systems are sold only where RF mitigation is permitted or required, and only with the applicable regulatory licenses and authorizations in place. SkyWall procurement requires a completed end-user certificate.
What legal authority is required to mitigate a drone?
In the United States, counter-UAS mitigation authority is granted by statute to a limited set of federal entities. The Department of War — still the Department of Defense as a matter of statute — and the Department of Energy operate under 10 U.S.C. § 130i; the Department of Homeland Security and Department of Justice operate under 6 U.S.C. § 124n. State and local law enforcement, and private operators, do not currently hold independent mitigation authority.
Detection carries no equivalent restriction, which is why detection-first architecture is the practical starting point for nearly every program. It also positions an organization to act quickly if authority expands, because the sensing layer is already in place and the mitigation layer integrates on top of it.
Deployment, acquisition, and the wider RF picture
How quickly can a system be deployed in the field?
SkyShield is built for rapid deployment. The dome configuration deploys and reaches operational status in field conditions in well under an hour, and the Mobile kit requires no installation at all — it operates from a vehicle, backpack, or tactical hardcase.
This supports temporary and expeditionary use cases directly: exercise support, emergency response, forward operating positions, mobile command posts, convoy and vehicle escort, and temporary event security.
Are there federal grants for counter-UAS programs?
Yes. The FEMA Counter-UAS Grant Program, established under the One Big Beautiful Bill Act of 2025, provides $500 million across two fiscal years. FY2026 prioritized $250 million for the eleven states hosting FIFA World Cup 2026 matches; the remaining $250 million opens in FY2027 to all 56 states and territories.
Eligible purchases include RF detection systems, radar, optical sensors, and tracking software. Mitigation equipment is additionally eligible for law enforcement agencies whose personnel are trained or enrolled at the FBI's National Counter-UAS Training Center — which is the practical route by which a state or local agency reaches mitigation capability.
For military and federal buyers, the JIATF-401 Counter-UAS Marketplace offers a streamlined procurement channel that sits on an existing IDIQ contract, letting authorized buyers acquire validated counter-UAS systems without working through separate acquisition pathways.
SAFE Perimeter supports grant scoping and application language, including the technical justification and system architecture sections that grant reviewers actually score.
Is SkyShield available on GSA Schedule?
Yes. The SkyShield product line — including SkyShield LR, SkyShield Mobile, SkyShield Sentry, and SkyWall — is available on GSA Schedule through our distribution partners, with first-year hardware and software support warranty included on the core systems.
Department of War, federal civilian, and state and local buyers can all acquire through this path. SAFE Perimeter supports acquisition from requirements definition through award, including sensor architecture, integration planning, and sustainment.
Why does wireless matter to installation defense beyond drones?
Because the same spectrum carries both problems. The aerial threat and the ground-level RF threat are visible to the same class of sensor, and installations that instrument only for drones leave the larger surface unmonitored.
Government environments have consistent gaps: limited in-house wireless and IoT expertise, air-gap assumptions that have never been validated against actual RF, SCIF and no-wireless zones enforced by policy rather than measurement, and a steady migration of control systems toward wireless and cloud connectivity. AirShield addresses these by proving whether an air gap is actually effective and whether a no-wireless zone is actually clean.
SAFE Perimeter supports requirements development, sensor architecture, and acquisition planning for installation defense and federal C-UAS programs.
Contact our government teamFor federal, state, and local law enforcement, corrections, protective services, and public safety agencies. Focus: technical surveillance countermeasures, RF device fingerprinting, executive protection, and mobile tactical kits.
TSCM — sweeps and covert device recovery
What is TSCM, and what happens during a bug sweep?
Technical surveillance countermeasures (TSCM) is the practice of detecting and neutralizing covert surveillance devices — hidden cameras, audio transmitters, GPS trackers, and unauthorized recording equipment — in a protected space. It is commonly referred to as a bug sweep or a debugging sweep.
Traditional TSCM is an event: a team arrives, sweeps, and leaves. The structural weakness is obvious in retrospect — a sweep certifies a room for the moment it ended. A device installed an hour later, or one that only transmits during the meeting it was placed for, will not appear in any sweep report.
A traditional sweep is a moment in time: scheduled, expensive, dependent on the specialist in the room, often limited to Wi-Fi and Bluetooth, and leaving little forensic record if something is found. The room is clean when they leave — and can be re-compromised minutes later. It also does not travel with the principal.
A standing watch is a posture rather than a visit: continuous and passive across 300 MHz to 6 GHz, surfacing threats in minutes with the device located for retrieval, and producing a time-stamped RF log that can be replayed after the fact. Modern practice pairs the two — periodic sweeps for physical inspection, continuous monitoring for everything between them.
What does a modern TSCM kit cover?
A current-generation TSCM capability has to cover the full range a covert device might use to exfiltrate — not just the Wi-Fi band. That means Wi-Fi, Bluetooth and BLE, cellular across 2G through 5G and LTE, LPWAN, GPS, and the sub-GHz bands used by cheap purpose-built transmitters and drone control links.
The SAFE Perimeter approach combines three elements:
- Broad-spectrum sensing across 300 MHz to 6 GHz, so a device is not missed because it uses an unexpected protocol.
- Classification — identifying vendor, protocol, and device type rather than just registering that something is transmitting.
- Direction finding and localization, so the team can physically recover the device rather than confirm one exists.
Handheld detectors give a proximity reading. Classification and localization are what turn a sweep into a recovery.
Digital suspect identification and RF forensics
What is digital suspect identification and RF device fingerprinting?
Most modern crimes involve a device — a phone, a drone, a wireless emitter. RF device fingerprinting identifies a specific device from the characteristics of its transmissions, with no access to the device itself and no cooperation from the network it uses. Digital suspect identification applies that capability investigatively: turning digital traces at a scene into leads.
What it produces is a persistent identifier for a device present at a location and time. That supports placing a device at a scene, establishing recurring presence, associating devices with one another, and building a pattern-of-life picture from RF alone — narrowing a suspect pool and linking individuals to network hardware.
With the proper legal authority, the platform can produce a digital fingerprint of an area, showing the devices, movements, and individuals present during an incident, and supporting a holistic reconstruction of events. The platform fingerprints across thousands of device types, including unauthorized hotspots, IoT devices, and drone control links.
Can RF detection data be used as evidence?
The platform produces time-synchronized forensic RF logs designed to support investigation, evidence building, and prosecution, with historical replay of the wireless environment. Whether a specific record is admissible in a specific proceeding is a question for the prosecuting authority and depends on jurisdiction, collection authority, and chain of custody.
What the technology provides is a defensible record: what was transmitting, when, on what protocol, and where — retained and replayable rather than reconstructed from memory.
IMSI detection and location
What is the LOCH Detector, and who can operate it?
The LOCH Detector is an IMSI catcher and locator built for special military and law enforcement operations. It detects and logs the IMSI numbers of nearby mobile devices, supports movement tracking and traffic analysis, and can locate GSM devices even in areas with no network coverage or difficult terrain.
It is available in man-portable, covert, vehicle, and UAV payload configurations. All units are built to MIL-STD-461F and MIL-STD-810G, IP67-rated, dual-channel minimum, Five Eyes compliant, and swarm-capable for coordinated multi-unit operations. Data is stored locally on the controlling workstation, encrypted with TLS/SSL and AES-256 over secure WebSockets, with no data retained on the detectors themselves.
Availability is restricted to qualified government and law enforcement end users with appropriate legal authority.
How is IMSI detection used in search and rescue?
Search and rescue teams use IMSI location to find missing individuals in disaster zones and remote areas where cellular coverage has failed. The system can create a private network, scan for devices in areas of no coverage, locate a device from authentication readings, and provide mapping data directly to rescue teams.
Teams can also place a voice call or send SMS to a located device, which converts a position estimate into confirmed contact with a survivor.
Mitigation authority for agencies
Can our agency mitigate, or only detect?
On the wireless layer, agencies can mitigate. AirShield and NetShield AI terminate unauthorized connections, isolate devices, and enforce access control policy against identified threats in facilities the agency controls — jails, evidence areas, task force spaces, dispatch centers, and protected venues. On the aerial layer, mitigation authority is federal and statutory; most state and local agencies do not hold it.
The practical consequence for a sheriff or a chief is that a counter-UAS program is a detection, geolocation, and interdiction-at-the-operator program, while a wireless program can be a full detect-and-respond program today.
Where aerial mitigation is required, the usual path is a federal partnership rather than an independent capability.
Why is targeted detection preferable to jamming?
Jamming is indiscriminate. It blocks all communication in its footprint, offers little control over what it affects, and commonly spills into adjacent areas and disrupts civilian networks — including the networks the responding agency itself depends on.
Detection-led approaches build an intelligence picture instead: identify the devices present, estimate their locations, and whitelist friendly numbers so that any subsequent action is precise rather than blanket. Operationally that means an agency keeps its own communications intact and can distinguish targets from bystanders.
In the field — corrections, executive protection, and mobile operations
How do you stop drones dropping contraband into a prison?
Contraband drops are an RF problem before they are an airspace problem. Detection catches the drone's control link during power-up and pre-flight — often while the aircraft is still miles outside the fence — classifies it against the 500-plus model library, and geolocates the operator so staff can direct a response to the launch point rather than the drop point.
Intercepting at the operator is the higher-value outcome. A recovered package removes one delivery; a located operator interrupts the supply route.
Corrections is one of the environments SkyShield is specifically built for, alongside law enforcement, airports, seaports, stadiums, and government facilities.
How does this support executive protection and VIP details?
Physical security is largely a solved problem for a protective detail. A detail controls the doors, the routes, and the room — but it cannot control the airwaves, and that is where modern surveillance against principals now lives. A camera the size of a shirt button. A tracker magnet-mounted under a bumper. A cell interceptor in the suite next door.
Coverage extends to the environments a principal actually moves through:
- Residence — estates, guest houses, staff quarters, and grounds
- Vehicle — motorcades, daily drivers, and hired cars
- Aircraft and yacht — cabins, hangars, marinas, and crew spaces
- Hotel and travel — suites, adjoining rooms, and event floors
- Office and boardroom — executive floors, deal rooms, and family offices
What it finds: hidden cameras concealed in rooms, fixtures, vehicles and gifts; listening devices on or off the network; cell interceptors positioned to capture calls and device identity; GPS trackers on vehicles, luggage, and personal effects; impersonated Wi-Fi and evil-twin traps; and camera drones over property lines, helipads, marinas, and arrivals.
The deployment model is one sensor at home and one in the bag. A discreet enclosure covers a residence, office, or cabin; an executive backpack carries the same capability through hotels, airports, and unfamiliar rooms — nothing on show, nothing to explain.
Discretion is itself a security control here. AirShield is entirely passive: it transmits nothing, interferes with nothing, and gives away no signature of its own, so the people watching your principal never learn that someone is watching back.
Can we deploy at a temporary event or from a mobile command post?
Yes. SkyShield Mobile is designed for exactly this — deployed from a vehicle, backpack, or tactical hardcase with no installation required, supporting emergency response, remote fieldwork, and mobile command posts. Sensors can backhaul over LTE where no network is available.
For fixed venues that host periodic events, a hybrid architecture is usually better economics: permanent sensors covering the core footprint, with mobile kits extending coverage to overflow areas, parking, and perimeter approaches on event days. Temporary installations also suit rooftop monitoring, high-profile gatherings, and National Special Security Events.
What training do our officers need?
Less than most agencies expect. SkyShield delivers situational awareness through desktop and mobile applications built for operational users rather than RF engineers, and SkyShield Sentry operates fully autonomously with no skilled operator required.
SAFE Perimeter provides comprehensive operator training as part of deployment, scoped to the configuration fielded and the roles that will use it. Partners additionally offer risk assessments, 24/7 NOC and managed services, operational support, and advanced training for agencies that want the capability without standing up an internal function.
Certain capabilities are restricted to qualified government and law enforcement end users. Contact us to verify eligibility and discuss requirements.
Contact our public safety team